AWS Solutions

manage terraform remote state aws

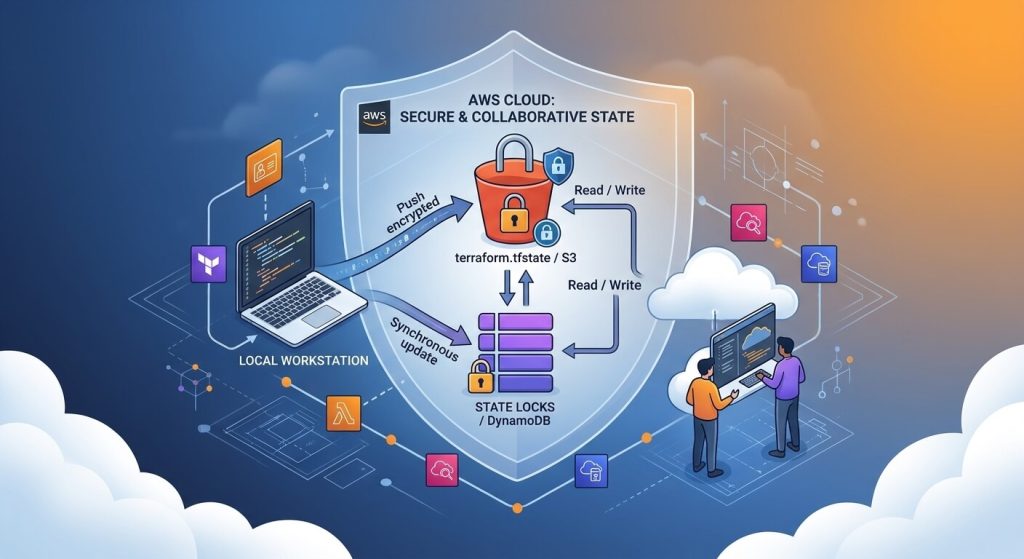
How to Manage Terraform Remote State in AWS: S3 & DynamoDB Best Practices

Introduction If you have been playing around with Terraform for a while, you probably started the exact same way I did: running terraform apply locally and watching that terraform.tfstate file pop up right there in your project folder. For quick local testing, it feels harmless. But the moment you start working with a team, or

How to Manage Terraform Remote State in AWS: S3 & DynamoDB Best Practices Read More »
Building a Complete Secure AWS Infrastructure with Terraform Step by Step Guide

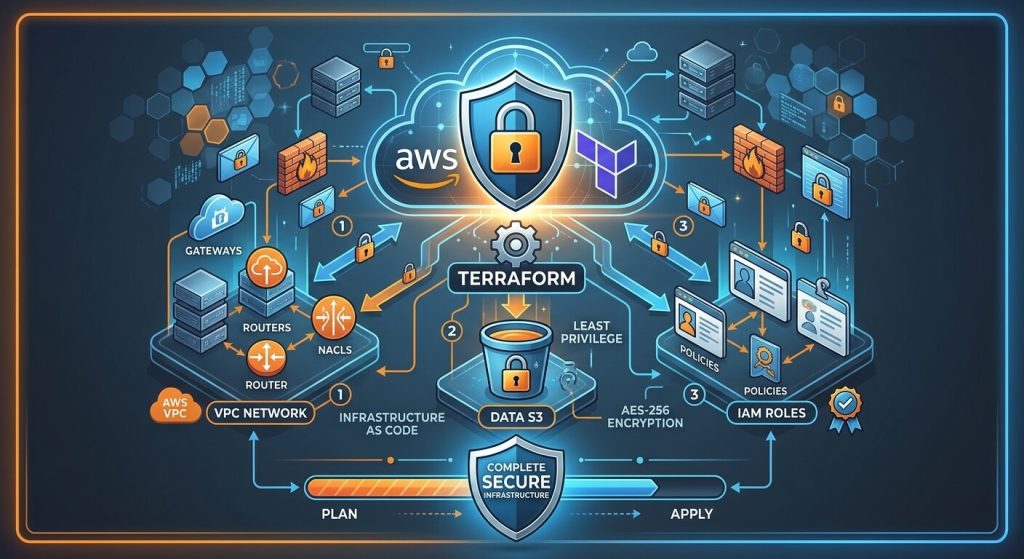
Building a Complete Secure AWS Infrastructure with Terraform: A Step-by-Step Guide

INTRODUCTION Building a secure cloud infrastructure manually through the AWS Console is time-consuming and leaves room for human error. Infrastructure as Code (IaC) solves this by letting you define, manage, and version your resources using clean configuration files. In this guide, we will use Terraform to build a complete, production-ready AWS environment from scratch—combining VPC

Building a Complete Secure AWS Infrastructure with Terraform: A Step-by-Step Guide Read More »

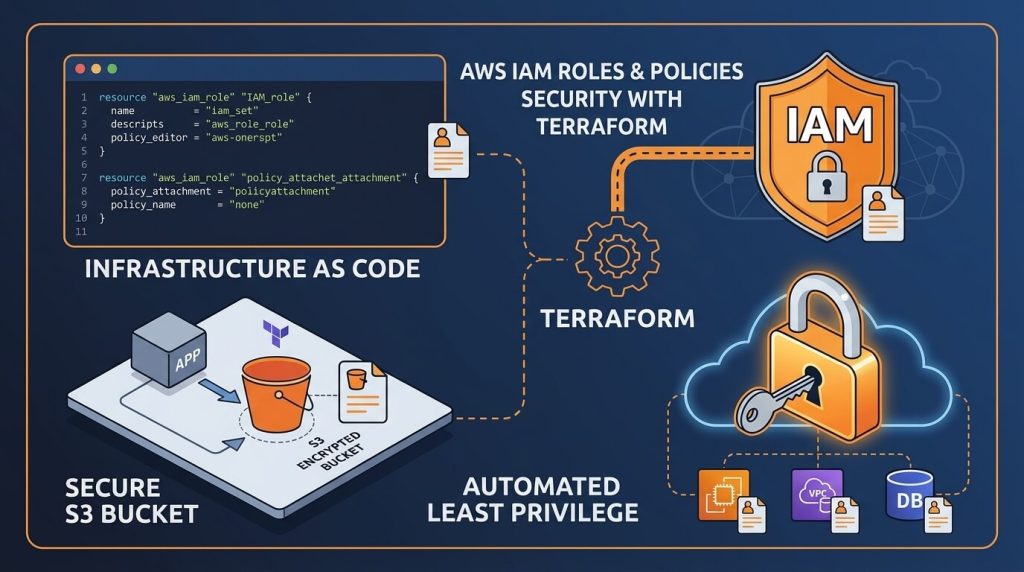
Provisioning AWS IAM Roles and Policies with Terraform for Secure S3 Access

Provisioning AWS IAM Roles and Policies with Terraform for Secure Cloud Access

INTRODUCTION Managing access control is one of the most critical pillars of cloud security. AWS Identity and Access Management (IAM) gives you fine-grained control over who can access your environment and what actions they can perform. Adhering to the principle of least privilege ensures that your applications receive only the exact permissions needed to function—nothing

Provisioning AWS IAM Roles and Policies with Terraform for Secure Cloud Access Read More »

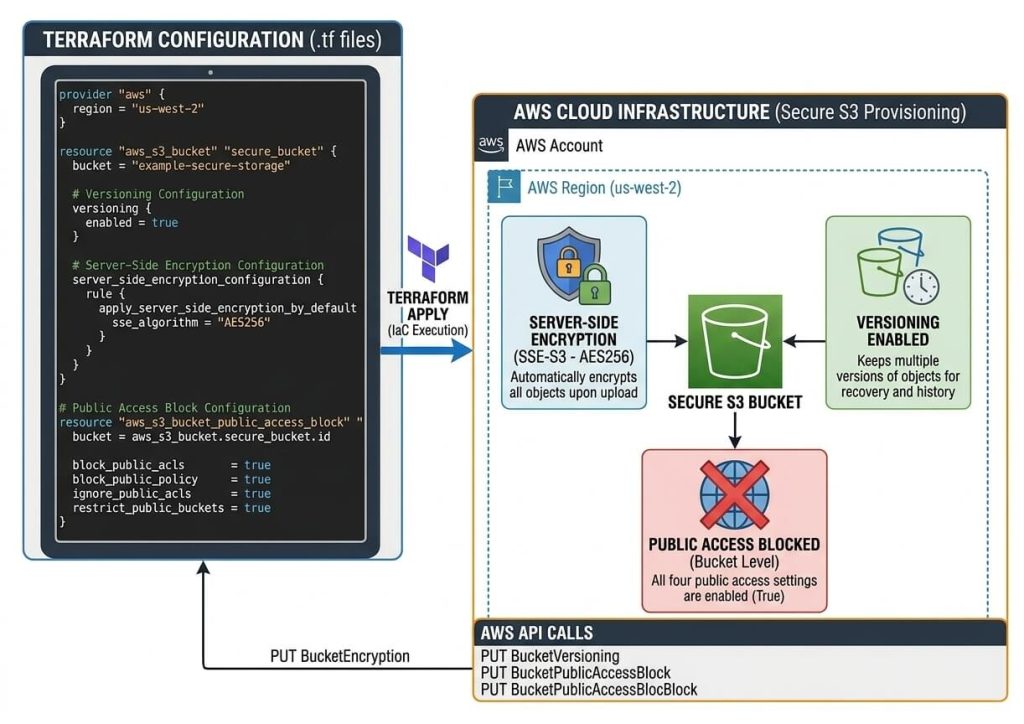
Provisioning Secure AWS S3 Bucket with Encryption and Versioning in Terraform

Provisioning Secure AWS S3 Buckets with Terraform for Application Storage

INTRODUCTION Every production-ready application needs a reliable place to store media files, user uploads, and backups. Following up on our previous guide where we provisioned an AWS RDS MySQL database, the next logical step in scaling our cloud setup is adding a dedicated object storage layer. In this tutorial, we will write clean, production-ready Terraform

Provisioning Secure AWS S3 Buckets with Terraform for Application Storage Read More »

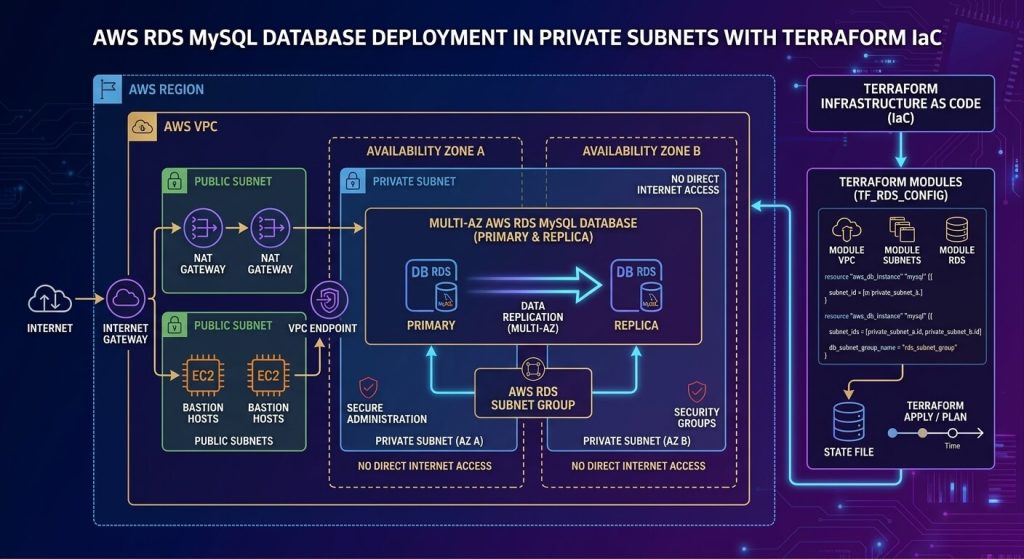
Provisioning AWS RDS MySQL Database with Terraform in Private Subnets

Provisioning AWS RDS MySQL Database with Terraform in Private Subnets

Introduction When designing a production-ready, multi-tier architecture on AWS, securing the backend layer is non-negotiable. Exposing a database to the open internet is one of the most common configuration risks. Building upon our previous guide on setting up EC2 instances within a custom AWS VPC, this hands-on tutorial focuses on isolating the database tier. We

Provisioning AWS RDS MySQL Database with Terraform in Private Subnets Read More »

Deploying EC2 instances in custom AWS VPC using Terraform

Deploying Highly Available EC2 Instances in Custom AWS VPC with Terraform

INTRODUCTION Building a robust cloud infrastructure requires more than just launching virtual servers—it demands placing those servers inside a securely architected network. Building upon our previous guide on AWS VPC Networking Fundamentals with Terraform, where we built a custom multi-tier network featuring both public and private subnets, we will now take the next logical step.

Deploying Highly Available EC2 Instances in Custom AWS VPC with Terraform Read More »

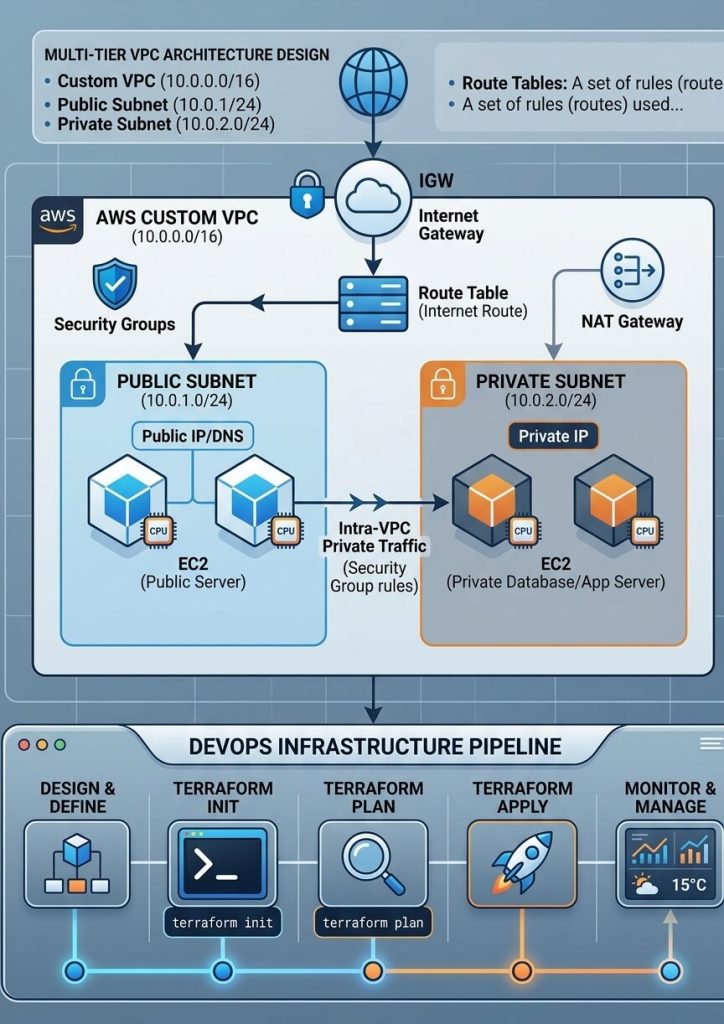
AWS VPC Networking Fundamentals with Terraform Architecture Diagram

AWS VPC Networking Fundamentals: Building a Custom VPC with Terraform

Networking is the foundation of any reliable cloud infrastructure. When working with Amazon Web Services (AWS), setting up a Virtual Private Cloud (VPC) gives you complete control over your network environment, allowing you to isolate resources securely. In this guide, we will build a secure, custom VPC from scratch using Terraform instead of configuring components

AWS VPC Networking Fundamentals: Building a Custom VPC with Terraform Read More »

AWS IAM Security Best Practices and Terraform Code Diagram

AWS IAM Security Best Practices: Managing Users, Roles, and Policies with Terraform

In cloud infrastructure, security is not an afterthought—it is the foundation. As organizations scale their infrastructure on Amazon Web Services (AWS), managing access control becomes critical. Without proper Identity and Access Management (IAM) controls, cloud environments become vulnerable to unauthorized access, data leaks, and severe security breaches. In our previous guide on Mastering Terraform Variables

AWS IAM Security Best Practices: Managing Users, Roles, and Policies with Terraform Read More »

Terraform variables, outputs, and secure state management best practices on AWS

Mastering Terraform Variables, Outputs & State Management (AWS Best Practices)

Hardcoding configuration values like Region, Instance Types, or Key Pair names directly into your main infrastructure file works fine for simple tests. However, as your infrastructure grows, hardcoded files become difficult to maintain, prone to human error, and insecure. In this hands-on guide, you will learn how to make your Infrastructure as Code (IaC) modular,

Mastering Terraform Variables, Outputs & State Management (AWS Best Practices) Read More »

Terraform vs manual AWS EC2 instance deployment comparison tutorial

Terraform vs. Manual AWS Console: How to Deploy Your First EC2 Instance in 10 Minutes (Step-by-Step for Beginners)

When you first start working with AWS, deploying a server usually means clicking your way through the web console. It’s intuitive and gets the job done, but it quickly becomes repetitive and doesn’t scale. That’s where Infrastructure as Code changes the game. In this walkthrough, we’ll skip the manual clicking and deploy your first EC2

Terraform vs. Manual AWS Console: How to Deploy Your First EC2 Instance in 10 Minutes (Step-by-Step for Beginners) Read More »